Dedicated Private Cloud on the Thalassa platform

The same cloud-native platform as Thalassa Public Cloud — IaaS, Kubernetes, databases, KMS, and more — on dedicated physical servers you control. On-prem, in a data center you choose, or dedicated in the Netherlands. Self-managed or managed. You keep the hardware, the perimeter, and the jurisdiction.

Nederlands · Product overview · Whitepaper

A full cloud platform, on hardware you control

Thalassa Private Cloud is a dedicated installation of the Thalassa Cloud platform. Your teams use the same console, APIs, CLI, and Terraform provider as on our public cloud. The difference is tenancy and placement: compute, storage, and the control plane run on dedicated physical infrastructure — in your building, in a data center you choose, or dedicated in Dutch data centers — isolated from other customers.

That model fits organisations that need fixed data residency, a dedicated security boundary, or the ability to offer cloud services to their own customers — including public-sector and regulated workloads that cannot sit on shared public cloud. Self-managed is a first-class option: license and updates, you operate.

How the platform is deployed

Capacity is measured in physical servers and availability zones, not in virtual-machine SKUs. The platform is licensed on that dedicated footprint — operations are self-managed, co-managed, or fully managed.

Footprint
Dedicated physical servers

A Private Cloud starts at four physical servers. License — and optional managed operations — scales with the number of servers.

Placement
On-prem, anywhere, or dedicated NL

Your building or edge, a data center you choose, or dedicated Dutch facilities. Start in a single site or stretch across availability zones. Jurisdiction follows the location you pick.

Hardware
Buy, lease, or bring your own

Hardware can be purchased, leased, or supplied by you, provided it meets Thalassa Cloud technical requirements. Capacity and redundancy are sized to the workload, not to a fixed SKU catalogue.

The same services as public cloud

A Private Cloud is not a hypervisor with a portal on top. It is the Thalassa platform: API-first infrastructure, Kubernetes, data services, and security controls that your platform teams already know how to automate.

Compute & containers

Virtual machines and managed Kubernetes, with a private container registry. Node pools, workload identities, and the same cluster lifecycle as on public cloud.

Kubernetes
Networking

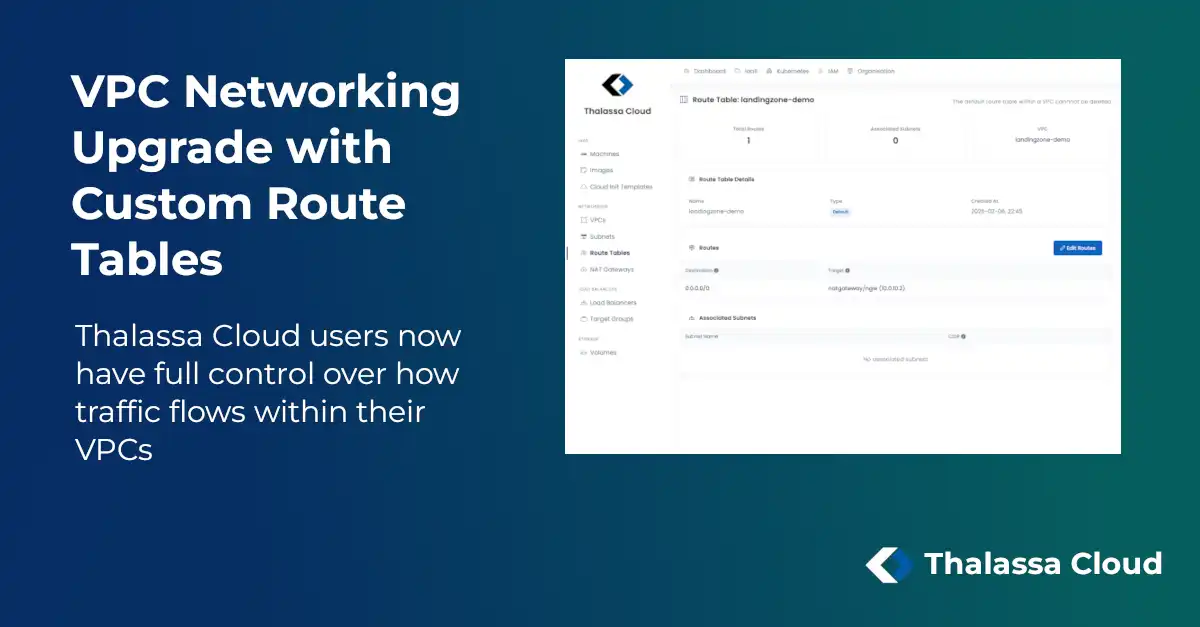
VPCs, security groups, firewalls, load balancers, NAT, DNS, and VPN. Dedicated physical network for the Private Cloud, exposed to users through the same VPC model and APIs.

VPCs
Storage & databases

Block storage, object storage, file storage, snapshots, and managed PostgreSQL — including backups and high availability — on the dedicated footprint.

PostgreSQL
Identity & key management

IAM, KMS, and Secrets Manager on the same control plane. Encryption keys and secrets stay inside the Private Cloud boundary.

KMS
Observability

Managed Prometheus and Managed Logging (Loki). Metrics and logs stay on the dedicated platform, with the same operational model as public cloud.

Automation

REST APIs, CLI, console, and a full Terraform / OpenTofu provider. New public-cloud services are intended to become available on Private Cloud deployments as the platform grows.

Infrastructure as Code

Who this is for

Organisations that need a modern cloud platform without giving up the perimeter.

Public sector

Public-sector organisations that need data residency, compliance, and a dedicated security boundary.

Banking & finance

Fixed residency, auditability, and a dedicated security boundary for regulated workloads.

CSPs and MSPs

A platform to offer cloud services from a location you choose, with the APIs your customers already expect.

Telecom & industry

Edge or on-site capacity with Kubernetes, networking, and storage under your operational control.

How a deployment is delivered

From design to a running platform on the sites you choose. The same team that builds the platform delivers the software — and, if you want, the on-site installation.

Step 1
Design

We translate your environment into a platform design: number of sites, physical servers, network, and identity. Setup follows that design, not the other way around.

Step 2
Platform setup

Control plane, platform services, IAM, and monitoring are configured. You get the same console, APIs, and Terraform provider as on public cloud.

Step 3
On-site installation

Self-managed: your team installs against our requirements. Or engineers visit each site: physical preparation, cabling and checks, provisioning, and commissioning. Hardware, rack space, and network follow the chosen location.

Step 4
Handover and lifecycle

Monitoring, administration, and operational handover. Updates then follow the same release train as public cloud. Extra integrations or hardening are delivered as engineering alongside the standard setup.

You decide how the platform looks

Thalassa Private Cloud is one platform with choices per environment. Capacity, sites, hardware, and operations scale with you — without a second stack.

Capacity
Start with four servers, grow per node

License and operations follow the number of physical servers. Additional nodes extend the same platform — growth does not require a redesign.

Locations
Your site, a chosen DC, or multiple AZs

Start on-prem, in a data center you choose, or dedicated in the Netherlands. Each site gets the same platform installation and the same operating model.

Hardware
Buy, lease, or bring your own

You choose the ownership model. We check that the configuration fits the platform — capacity and redundancy follow the workload, not a fixed catalogue.

Operations
Self-managed, co-managed, or fully managed

License and updates as the baseline. You operate, we co-operate, or we run platform operations. Service management, NOC, and 24/7 cover are added when the environment becomes production — not as a condition to start.

Network
Dedicated network in the VPC model

Own IP prefixes and dedicated internet. You manage routes and security groups through API and Terraform, the same as the rest of the platform.

Connectivity
Custom network connections

Not only public internet. We design dedicated network connections that land in the VPC model, so your teams consume them through API and Terraform.

Ready to scope a dedicated platform?

We will map servers, sites, self-managed or managed operations, and connectivity to a design you can take through procurement — without locking you into a hyperscaler stack. No public price list.

Talk to an engineer Product overview Whitepaper Nederlands

Related articles

Ready to take control of your Cloud Infrastructure?

Talk to one of our engineers

Please contact us for more information about the Thalassa Cloud Platform.
form will be placed in here